Threat hunting: 10 principles for finding the attackers your alerts miss
Why is threat hunting so important? What happens when an attacker gets into your environment and none of your security tools notice? Adam Wong, Senior Security Analyst for Threat Intelligence and Threat Hunting at ISA Cybersecurity, encourages organizations to run threat hunting exercises so they find potential incidents sooner. In this article, Adam shares the […]
Kevin Dawson to retire as President and CEO of ISA Cybersecurity; Andrew Buckles to succeed him
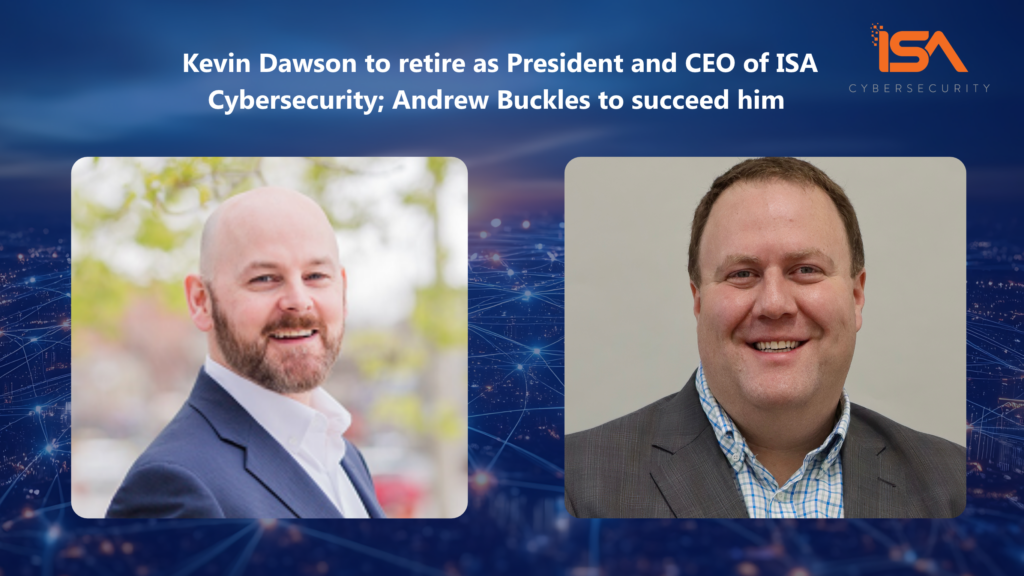
Today, ISA Cybersecurity announces a planned leadership transition years in the making. Kevin Dawson, ICD.D, will retire as President and CEO on December 31, 2026, after 28 years with the company and more than 12 at its helm. He hands the role to Andrew Buckles, who will become President and CEO on January 1, 2027, […]
Five Lessons Learned from the LiteLLM Supply Chain Attack
Forty minutes. That’s how long two poisoned versions of LiteLLM sat on the Python Package Index on March 24 before they were pulled… and how long it took to strip secrets out of software build pipelines at thousands of companies around the world. Five months later, the names of those companies are coming to light. […]
Breaches at Machine Speed: A Canadian Read on IBM’s 2026 Cost of a Data Breach Report
IBM has just released its Cost of a Data Breach Report 2026, subtitled “The AI tipping point.” The story in the numbers is one every security team will recognize: attackers are moving faster, and their victims are paying more. In Canada, the picture is worse than the global average. The average breach now runs $5.20 […]
Bill C-8 and the New Cybersecurity Reality in Canada
Canadian organizations are already dealing with ransomware, supply chain compromise, AI-enabled phishing, regulatory pressure, cyber insurance scrutiny, and growing expectations from boards and customers. Bill C-8 adds another layer to that environment, but it also signals something larger: cybersecurity has grown from an internal IT governance concern into a core element for national infrastructure policy. […]
Securing Agentic AI Identities: Four Things You Need to do Tomorrow
For years, identity security was built primarily around human users requesting access. In the old model, identity was largely deterministic. A user or service account mapped to a known role, a known system, and a predictable set of actions. Even non-human identities were tightly scoped and relatively static. Governance could afford to be periodic because […]
Bridging the Frameworks: How NIST CSF and AI RMF Work Together to Help Manage AI Risk
As organizations race to adopt artificial intelligence, a practical question follows: how do you govern something that evolves this quickly? Many organizations find themselves caught between the urgency of AI adoption and the need to deploy responsibly. Fortunately, if you are already familiar with the NIST Cybersecurity Framework (CSF), you have a strong head start […]
The CPCSC Is Live
What Canadian Defence Suppliers Need to Do Next Nitin Bedi, ISA Cybersecurity’s VP, Services revisits the Canadian Program for Cyber Security Certification (CPCSC) as Phase 2 of the rollout takes effect, and outlines the practical steps organizations should be taking right now. Amid all the attention on Mythos Preview and Project Glasswing in early April, […]
The Preventable Breach: The Importance of Strong Vulnerability and Patch Management
The Importance of Strong Vulnerability and Patch Management The digital forensics team’s report lands on your desk in the quiet aftermath of a data breach. You open it, scanning past timelines and technical details, searching for the answer everyone’s been asking: How did they get in? Your heart sinks when you realize that the attacker […]